How Long Must Monitoring Sensor Data Be Kept? Retention, Archiving, and Audit Trails
Environmental monitoring data retention guide: KLHK regulations, ANRI standards, a 3-layer storage model, and ALCOA+ principles for audit readiness.
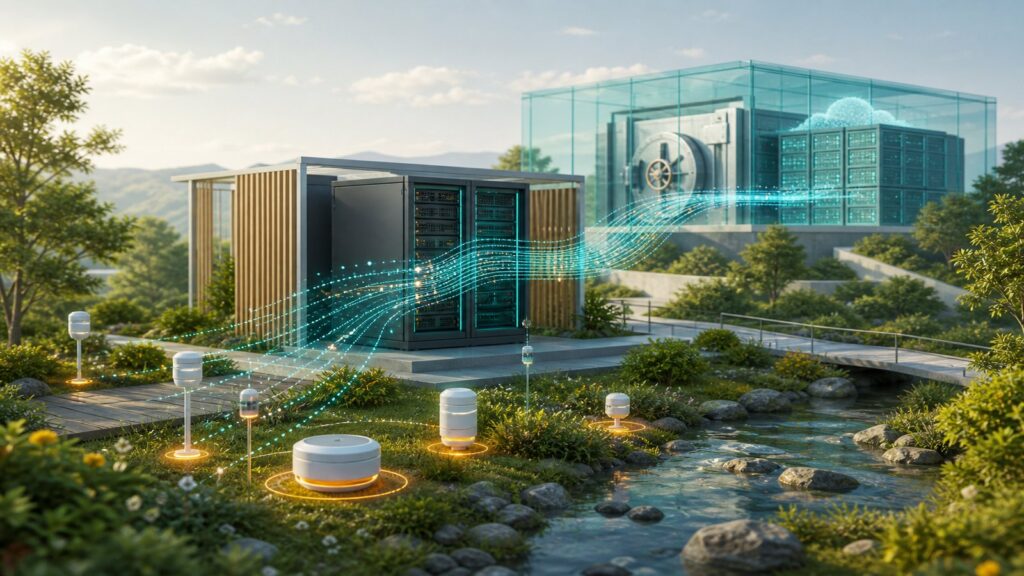
Indonesia’s SPARING regulation (PermenLHK P.93/2018) forces data loggers to store and transmit sensor readings to the government server. But it leaves a massive blind spot: it never actually sets a monitoring data retention period. The regulation tells you to record the data and send it, but ignores how long you have to keep it, where it goes after transmission, or how you prove it wasn’t tampered with during an audit.
That gap is dangerous. A facility logging pH, TSS, and COD every two minutes will still fail an audit if they cannot produce a clean historical record from three years ago because a server overwrote it.
We are going to map out the actual regulatory landscape, build a practical three-layer storage architecture, and apply a strict data integrity framework to close the gap between “we transmitted it” and “we can prove it.”
The Regulation Doesn’t Say How Long. So Who Decides?
PermenLHK P.93/2018 wrote the technical playbook for Indonesia’s SPARING continuous monitoring network. Loggers must sample, store, and transmit. The 2019 amendment (PermenLHK P.80/2019) added more industries and tightened sensor specs. But neither rule specifies how many months or years you actually have to hold onto your records.
The real answer lives in a completely different regulatory domain. ANRI (Arsip Nasional Republik Indonesia)—the national archives authority—publishes retention schedules called Jadwal Retensi Arsip (JRA). ANRI Perka 47/2015 handles regional government records and classifies environmental monitoring data under a specific tier: 5 years of active retention, followed by transfer to a permanent archive. This rule governs the data SPARING facilities generate and regional agencies collect.
KLHK runs its own internal archival schedule under PermenLHK P.21/2017, though you have to dig through the annexes to see exactly how they handle continuous telemetry data internally.
Look at how other countries do it. The U.S. EPA enforces a hard 3-year minimum for NPDES monitoring records (40 CFR 122.41(j)(2)). ISO 14001:2015 (Clause 7.5) demands you retain documented environmental info but lets the organization pick the timeline. Indonesian facilities caught under ANRI’s framework actually face a much stricter standard.
Regulations shift constantly. The periods I cite here reflect the rules as of September 2026. Check the current legal texts before you write your company’s retention policy.
Three Storage Layers: Device Buffer, Server, and Archive
You cannot force 5 years of retention onto a single piece of hardware. It requires a layered approach.
Layer 1 — Device buffer (hours to days). The data logger runs a rolling buffer of recent readings. This is volatile, short-term memory built specifically to survive network dropouts. If the cell signal dies, the buffer holds the data until the connection comes back. (Read more on how this works in our guide to data logger storage). Device buffers ruthlessly overwrite old data when they fill up. They are vulnerable to power loss, lightning strikes, and physical tampering. They are not an archive.
Layer 2 — Operational server or cloud (months to 5 years). Once the logger pushes the data, it lands on a server or cloud platform. This is where operators run queries, build dashboards, and pull compliance reports. Retention here covers the ANRI active period: up to 5 years of hot, accessible data. Backups, user access controls, and version-tracked databases live at this layer.
Layer 3 — Long-term archive (5+ years, permanent). When the active window closes, data moves to read-only cold storage. Speed does not matter here; durability does. You use write-once media, cryptographic hash verification, and locked-down access controls to ensure nobody alters the history. Under ANRI’s “permanent archive” rule, you don’t delete this data. You keep it retrievable forever.
This three-layer model is not a legal mandate. It is a practical engineering framework. The hardware you use at each layer depends entirely on your budget and scale. What matters is that your architecture handles all three phases and maintains a clean chain of custody as data moves between them.
ALCOA+ for Environmental Sensor Data Integrity
ALCOA+ is a data integrity framework built by the pharmaceutical industry (GxP regulations). But its nine rules apply perfectly to any system that has to survive a brutal regulatory audit, including environmental monitoring.
Here is how the nine principles translate to sensor data:
| Principle | Meaning | Application to Sensor Data |
|---|---|---|
| Attributable | Every record traces to a person or system | Sensor ID, data logger serial number, and operator login recorded with each data point |
| Legible | Data is readable and permanent | Stored in non-proprietary formats; timestamps in ISO 8601; no handwritten overrides |
| Contemporaneous | Recorded at the time of the event | Data logger timestamps synchronized via NTP; no retroactive manual entry |
| Original | First-captured record preserved | Raw sensor output retained separately from processed or averaged values |
| Accurate | Data reflects the true measurement | Calibration records linked to each sensor; data quality flags applied |
| Complete | No gaps or selective deletion | Offline detection logs periods of missing data; gap reports generated automatically |
| Consistent | Data agrees across copies and systems | Hash verification between device buffer, server, and archive; edge validation checks at ingestion |
| Enduring | Records survive for the full retention period | Migration plan from active server to long-term archive; media integrity checks |
| Available | Data is accessible when needed | Indexed archive with retrieval procedures documented; access within reasonable time for audit requests |
ALCOA+ is not an Indonesian law. It is just the gold standard for proving your data isn’t faked. When an auditor from KLHK, a regional agency, or an ISO certification body walks in, they are looking for exactly what these principles describe. Build your procedures around ALCOA+ now, so you aren’t scrambling when the regulations eventually mandate it.
What Does an Auditor Actually Check?
When a regulatory inspector starts digging through your monitoring records, they ask the same questions every time. You need the answers ready before they ask them.
Timestamp integrity. Are the readings timestamped the second the probe touched the water, or when the server finally received the packet hours later? Are the time zones consistent? Do you have proof that the data logger clock is locked to a reliable NTP server?
Chain of custody. Can you prove exactly how a specific data point moved from the sensor, through the logger, across the network, and into the archive? If a technician modified a value, does the system log the original number next to the amended one?
Calibration linkage. When an auditor points to a specific reading from two years ago, can you produce the exact calibration record for that sensor on that day?
Data completeness. Do you have a log explaining every gap in the data? Routine maintenance, a dead modem, a severed cable—every offline minute needs a timestamped reason. A documented outage is annoying; an unexplained gap looks like fraud.
Access controls and amendment logs. Who has the admin password? If someone deletes a row of archived data, does the audit trail log their name, the exact time, and the reason they gave?
Practical Steps for Audit Readiness
You do not have to fix your entire data architecture this afternoon. Take these three steps to build a defensible retention posture.
First, assess your current retention. Figure out where your sensor data actually lives right now: a logger buffer, a local server, a cloud dashboard, or a folder full of CSV files. Find the oldest retrievable record for each parameter. Compare that date against the ANRI 5-year active retention benchmark. If you cannot pull data from 6 months ago because a server overwrote it, you have a massive compliance gap.
Second, map the data flow. Write down exactly how a reading gets from the river to the archive. Find every spot where the system averages, transforms, or copies the data. Each of those spots is a potential chain-of-custody failure. Draw a simple diagram (sensor → logger → server → archive) and write the retention time and the person responsible next to each step.
Third, use ALCOA+ as an internal checklist. Test your real records against the nine principles. You will probably find missing calibration links and undocumented offline gaps immediately. Fix those first. Force the rest of the principles into your operating procedures one at a time.
You don’t need to buy new hardware to do this. You just need discipline, documentation, and the understanding that data retention isn’t about buying a bigger hard drive. It is about generating a record an auditor is forced to believe.
Share this article
Share this insight with your team.
Related Articles
Similar topics from the same category.
Poor weather station placement can cause 50% data bias. Learn the WMO-No. 8 and Indonesian BMKG siting standards for AWS sensors in industrial and mining sites.
Explore a technical engineering comparison between solid-state ultrasonic anemometers and mechanical cup-and-vane sensors for industrial weather stations.
Technical guide to conductivity sensors: comparing toroidal (inductive), 2-electrode, and 4-electrode contacting probes for industrial water and wastewater.